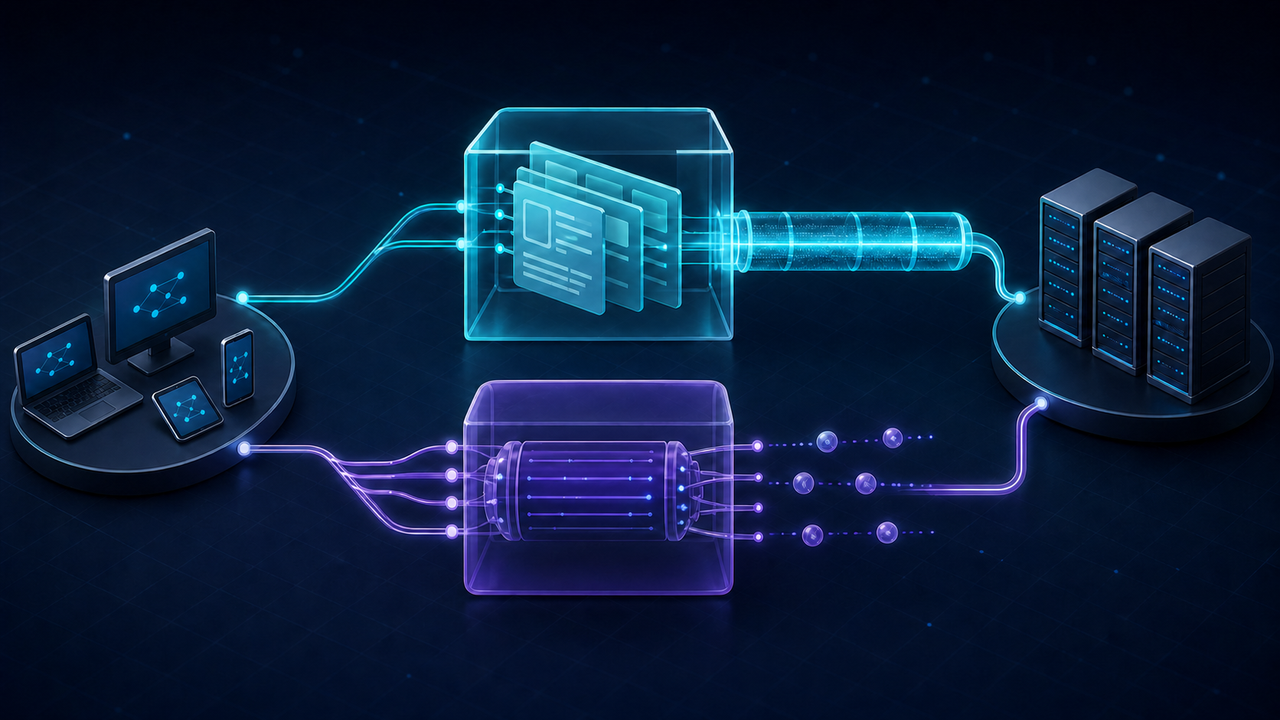
Choose an HTTP proxy when the workload is web-only and the client expects an HTTP or HTTPS proxy setting. Choose SOCKS5 when a compatible client must carry non-HTTP TCP traffic or send destination hostnames to the proxy for resolution. For ordinary HTTPS traffic, either option can carry end-to-end TLS to the destination; test the real route before deciding on performance.
Side-by-side comparison
Dimension | HTTP proxy | SOCKS5 proxy |
|---|---|---|
Primary layer | HTTP-aware interface | General relay between application and transport |
Typical traffic | HTTP and HTTPS via CONNECT | Multiple TCP protocols; optional UDP relay |
DNS behavior | Depends on client and proxy mode | Client may send an IP or hostname |
Authentication | HTTP proxy authentication, commonly 407 challenge | Method negotiation; username/password is optional |
Application awareness | Can process plain HTTP messages | Does not define application-message parsing |
Best fit | Web clients and HTTP-aware policy | Mixed protocols and explicit SOCKS-capable clients |
Encryption | Not inherent; use HTTPS/TLS | Not inherent; use end-to-end secure protocols |
Choose an HTTP proxy when
- The workload is primarily HTTP or HTTPS.
- The client exposes only HTTP/HTTPS proxy settings.
- You need HTTP-aware authentication, logging, filtering, caching, or request policy.
- A conventional CONNECT tunnel is sufficient for HTTPS traffic.
Choose SOCKS5 when
- One proxy interface must relay several TCP application protocols.
- A compatible application requires SOCKS5 UDP ASSOCIATE.
- The client must send destination hostnames to the proxy for resolution.
- The application explicitly supports SOCKS5 or a compatible wrapper is available.
Use the comparison above to narrow your options, then follow the setup and DNS checks below to verify your proxy configuration.
What each proxy does
For plain HTTP, an HTTP forward proxy can receive and forward HTTP messages. For HTTPS, a conventional proxy accepts CONNECT and creates a TCP tunnel; the client then establishes TLS with the destination through that tunnel.
SOCKS5 begins with method negotiation, then the client requests CONNECT, BIND, or UDP ASSOCIATE for an IPv4 address, IPv6 address, or domain name. It can relay HTTP, TLS, SSH, or another protocol when the application supports SOCKS.
Data flow
Plain HTTP
Client -- HTTP request --> HTTP proxy -- HTTP request --> Origin

HTTPS through an HTTP proxy
Client -- CONNECT host:443 --> HTTP proxy --> Origin
Client ============== TLS through the tunnel ============= Origin

SOCKS5
Client -- method negotiation + target request --> SOCKS5 proxy
Client <============ TCP or supported UDP relay ==========> Target
HTTP proxy, HTTPS destination, and TLS to the proxy are different
The words HTTP and HTTPS can describe different hops. An HTTP proxy can still tunnel an HTTPS destination with CONNECT. An HTTPS proxy endpoint adds TLS between the client and proxy, but the destination also needs HTTPS when the application payload must remain encrypted end to end.
Path or term | Client to proxy | Proxy to destination | What is protected |
|---|---|---|---|
HTTP proxy to an HTTP destination | Plain HTTP proxy protocol | Plain HTTP | No encryption is inherent |
HTTP proxy to an HTTPS destination | HTTP CONNECT control, then a tunnel | TLS terminates at the destination | HTTPS payload is protected between client and destination |
HTTPS proxy endpoint (TLS to proxy) | TLS protects the client-to-proxy hop | HTTP forwarding or CONNECT tunnel | Proxy credentials and control traffic are protected on the first hop; destination HTTPS is still required for end-to-end payload protection |
SOCKS5 proxy to an HTTPS destination | SOCKS5 negotiation and relay | TLS terminates at the destination | HTTPS payload is protected end to end; SOCKS5 negotiation is not encrypted by the protocol itself |
If the task needs a longer-lived ISP exit, compare static residential proxies and confirm that your client supports the chosen protocol.
DNS behavior matters
SOCKS5 does not automatically guarantee remote DNS. The client can resolve locally and send an IP, or send a hostname for proxy-side resolution. In curl, socks5:// resolves locally while socks5h:// sends the hostname through the proxy.
You can check DNS records online with NSLookup. Use the curl modes below to distinguish client-side and proxy-side resolution.
# HTTP proxy; curl uses CONNECT for this HTTPS URL
curl --proxy http://proxy.example:8080 https://example.com/

# SOCKS5 with local destination DNS
curl --proxy socks5://proxy.example:1080 https://example.com/

# SOCKS5 with hostname sent to the proxy
curl --proxy socks5h://proxy.example:1080 https://example.com/
Reproducible curl checks
The checks below were recorded on Windows with curl 8.16.0. The commands use PowerShell environment variables and placeholder connection details; substitute an authorized endpoint without storing credentials in the article or shell history.
1. Check an HTTP proxy
$env:PROXY_HOST = "[redacted-proxy-host]"
$env:HTTP_PROXY_PORT = "[redacted-port]"
$env:SOCKS5_PROXY_PORT = "[redacted-port]"
$env:PROXY_USER = "[redacted-user]"
$env:PROXY_PASS = "[redacted-password]"

curl.exe --fail --show-error --silent `
  --proxy "http://${env:PROXY_HOST}:${env:HTTP_PROXY_PORT}" `
  --proxy-user "${env:PROXY_USER}:${env:PROXY_PASS}" `
  --output NUL --write-out "status=%{http_code} total=%{time_total}s`n" `
  "https://example.com/"
Recorded 2026-09-05 UTC (sanitized):
status=200 total=0.856s2. Check SOCKS5 with local destination DNS
curl.exe --fail --show-error --silent --verbose `
  --proxy "socks5://${env:PROXY_HOST}:${env:SOCKS5_PROXY_PORT}" `
  --proxy-user "${env:PROXY_USER}:${env:PROXY_PASS}" `
  --output NUL --write-out "status=%{http_code} total=%{time_total}s`n" `
  "https://example.com/"
Recorded 2026-09-05 UTC (sanitized):
* Host example.com:443 was resolved.
* IPv4: [redacted-ip]
< HTTP/1.1 200 OK
status=200 total=1.323s3. Check SOCKS5 with proxy-side destination DNS
curl.exe --fail --show-error --silent --verbose `
  --proxy "socks5h://${env:PROXY_HOST}:${env:SOCKS5_PROXY_PORT}" `
  --proxy-user "${env:PROXY_USER}:${env:PROXY_PASS}" `
  --output NUL --write-out "status=%{http_code} total=%{time_total}s`n" `
  "https://example.com/"
Recorded 2026-09-05 UTC (sanitized):
(no local “Host example.com:443 was resolved.” or “IPv4: …” line)
< HTTP/1.1 200 OK
status=200 total=1.997sIndependent direct-versus-proxy exit check
A separate check at 2026-09-05T08:46:06Z sent one direct request and one request through the HTTP proxy. Both requests succeeded, and the sanitized comparison confirmed that their exit addresses were different.
Recorded 2026-09-05T08:46:06Z (sanitized):
direct_request=success exit=[redacted-direct-ip]
http_proxy_request=success exit=[redacted-proxy-ip]
same_exit=false
The recorded values document only these individual connections. The SOCKS5 run showed local destination resolution, while the SOCKS5H run omitted the local Host-resolved and IPv4 lines before returning HTTP/1.1 200. To compare performance, repeat the same authorized request on the same network, report sample size and variability, and avoid treating these three timings as a ranking.
Troubleshooting protocol, port, and authentication errors
Symptom | Likely cause | Check and fix |
|---|---|---|
HTTP 407 Proxy Authentication Required | Missing, rejected, or incorrectly encoded credentials | Confirm the assigned username and password; quote the proxy URL and percent-encode reserved characters instead of printing credentials in logs |
Connection refused or timeout immediately | Wrong proxy port, wrong protocol scheme, firewall, or unreachable endpoint | Confirm the provider-assigned host, port, and protocol; test TCP reachability without repeatedly rotating endpoints |
Unsupported proxy syntax or option | The client build lacks SOCKS support or uses different settings | Run curl --version and check the client documentation; upgrade or use a supported HTTP proxy mode |
socks5h works but socks5 fails | The local resolver cannot resolve the destination or DNS is blocked | Check the local resolver; use proxy-side DNS deliberately when policy permits it |
TLS certificate error | Destination certificate issue or unexpected TLS interception | Inspect the certificate chain and proxy policy; do not hide the problem with --insecure |
Security considerations
- A proxy is not encryption. Use HTTPS, SSH, or another end-to-end secure protocol.
- RFC 1929 username/password authentication does not encrypt the password by itself.
- Local DNS can expose destination queries outside the proxy path; remote DNS transfers that visibility to the proxy operator.
- Restrict CONNECT targets, SOCKS relay destinations, credentials, and network access.
- Do not confuse a normal CONNECT tunnel with an explicitly governed TLS-interception proxy.
Frequently asked questions
Is SOCKS5 safer or more anonymous than HTTP?
Not by protocol name alone. End-to-end encryption, DNS mode, authentication, logging, client behavior, and operator trust determine the security outcome.
Can an HTTP proxy handle HTTPS?
Yes. A conventional HTTP proxy uses CONNECT to create a TCP tunnel, then TLS runs between the client and destination through it.
Can SOCKS5 carry HTTP and HTTPS?
Yes, when the client supports SOCKS5. The proxy relays the connection without needing to interpret HTTP.
Does SOCKS5 always prevent DNS leaks?
No. The client may resolve locally. Use an explicit proxy-side DNS mode such as socks5h in curl and verify deployed behavior.
Does an HTTP proxy support UDP?
Do not assume it. Classic CONNECT is TCP. CONNECT-UDP is a separate extension that requires compatible client and proxy support.
Which proxy is faster?
There is no universal winner. Benchmark the real route, concurrency, connection reuse, DNS mode, and protocol mix.
Use the protocol your workflow actually needs
Verify client compatibility, DNS behavior, authentication, and end-to-end encryption before rolling out a proxy configuration.