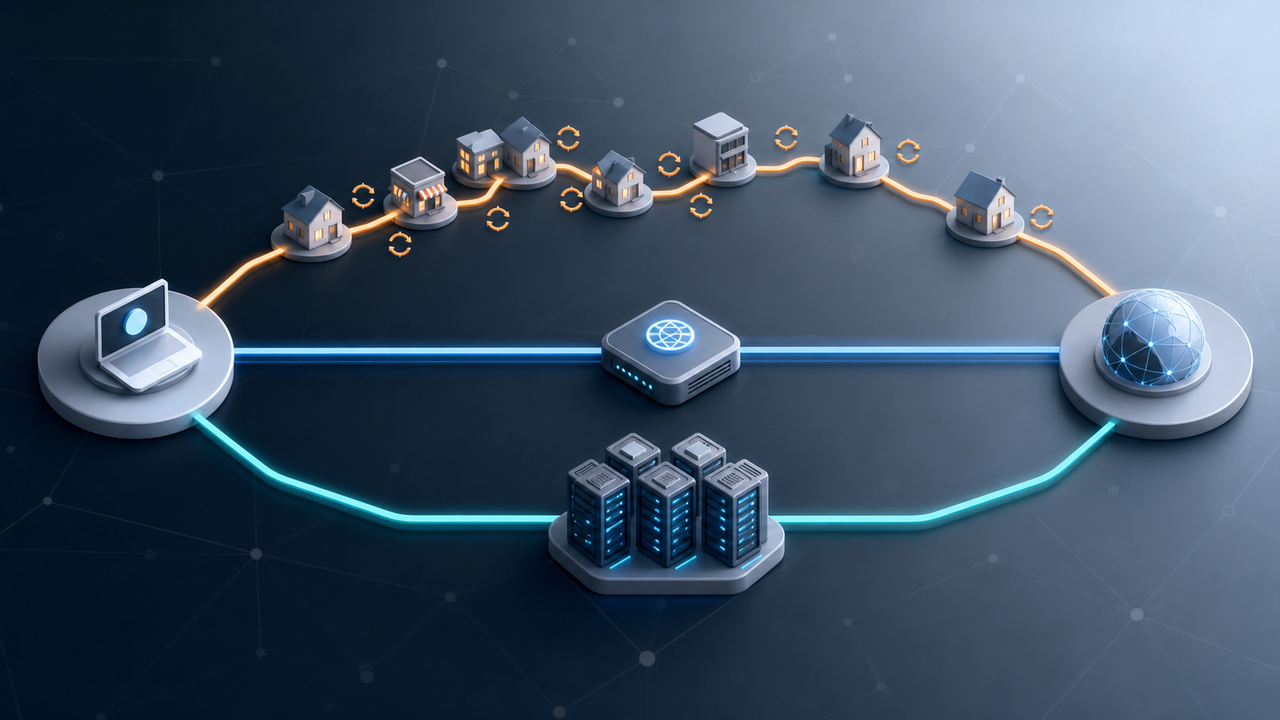
Choosing a proxy is not only a residential-versus-datacenter decision. You must separate two questions: where the exit IP comes from, and whether the service keeps or rotates that exit. This guide compares dynamic residential, static residential or ISP, and datacenter proxies for authorized workloads.
Product labels are not IETF protocol categories. Providers can implement rotation, sticky sessions, sharing, and dedicated allocation differently, so verify the actual contract rather than relying on the name alone.
Two independent axes: IP source and exit behavior
First choose the network source the authorized workload actually needs. Then choose how long the exit should remain stable. Treating these as separate decisions prevents a common mistake: assuming every residential proxy rotates or every datacenter proxy is static.
Decision axis | Options | What it controls | What it does not guarantee |
|---|---|---|---|
IP source | Residential last-mile, ISP-registered, or datacenter | Network ownership, route context, and available locations | Rotation frequency, dedication, or session lifetime |
Exit behavior | Rotating, bounded sticky session, or static allocation | When and how the exit IP changes | Residential or datacenter origin, reputation, or access |
Source × behavior matrix
IP source | Rotating | Sticky session | Static |
|---|---|---|---|
Residential pool | Common for independent regional requests | Common for a bounded multi-request flow | Not implied by “residential”; verify the allocation model |
ISP-registered infrastructure | Provider-specific | Possible when the service exposes session controls | Commonly sold as static residential or ISP proxy |
Datacenter infrastructure | Available as rotating pools | Provider-specific | Common as dedicated or shared fixed endpoints |
What a forward proxy changes
A client authenticates with a proxy gateway. The gateway selects an exit according to location, pool, and session policy, then connects to the permitted destination. The destination sees the exit IP, but can still evaluate account, browser, request, and reputation signals.
Client -> authenticated gateway -> selected exit IP -> authorized destination
                              ^
                              | rotation, sticky session, or fixed allocation
Three proxy models at a glance
Dimension | Dynamic residential | Static residential / ISP | Datacenter |
|---|---|---|---|
Typical source | Residential-network pool | ISP-registered fixed allocation | Hosting or cloud network |
Session behavior | Rotating or time-limited sticky | Long-lived assigned address | Fixed, shared, or rotating |
Primary strength | Regional and address diversity | Session and location continuity | Throughput and cost control |
Operational trade-off | Variable nodes and latency | Smaller inventory; reputation accumulates | Hosting ASN is easier to classify |
Best fit | Independent regional checks | Authorized multi-step sessions | APIs, CI, monitoring, bulk permitted traffic |
Common billing | Usually by traffic | Usually by IP and period | Usually by IP, port, or traffic |
Always verify | Pool provenance and session limits | Allocation, replacement, and expiry policy | Sharing, concurrency, and bandwidth limits |
Dynamic residential: prioritize coverage and diversity
Dynamic residential services expose a gateway backed by a changing residential pool. Rotation works for independent regional checks; a sticky session can keep one exit for a limited workflow. Node availability, latency, geolocation, and session lifetime can vary, so measure them with representative traffic.
Static residential or ISP: prioritize continuity
A static residential or ISP proxy assigns one ISP-registered address for a longer period. It can support authorized multi-step sessions, repeatable regional QA, or stable allowlisting. A fixed address still accumulates reputation and can expire or be replaced under provider policy.
Datacenter: prioritize efficiency
Datacenter proxies originate from controlled server infrastructure. They are often the clearest starting point for owned-system monitoring, CI, APIs, permitted downloads, and high-throughput tasks that do not require residential network context. Actual performance still depends on routing, sharing, concurrency, and destination policy.
For the MIYAIP option, compare dedicated datacenter proxies and review the plan duration and inventory before buying.
A practical selection rule
- Use dynamic residential when multiple regions or diverse residential exits are a real requirement and requests are mostly independent.
- Use static residential or ISP when an authorized workflow needs both ISP network context and a consistent long-lived exit.
- Use datacenter when speed, capacity, predictable infrastructure, or cost matters more than residential origin.
- Pilot the smallest suitable option and measure latency, error rate, location accuracy, session lifetime, and cost per successful task.
Three conditional workload cases
1. Continuous multi-step session
If an authorized login, cart, or QA flow must keep one exit, choose a static or sufficiently long sticky allocation. Use static residential or ISP only when ISP network context is part of the test; if the requirement is simply a stable or allowlisted IP, a dedicated datacenter endpoint is usually simpler.
2. Distributed request collection
If many independent requests must sample several permitted regions, a rotating residential pool can supply location and network diversity. If consumer-network origin is irrelevant and the destination permits automation, a rotating or sharded datacenter pool can reduce complexity. Set conservative concurrency and measure regional availability.
3. Cost-sensitive public-data workload
Start with datacenter for permitted public data when neither residential origin nor a long-lived ISP identity is required. Compare a representative pilot before switching: lower unit price can lose its advantage if retries, incomplete tasks, or operator time rise.
Hypothetical cost worksheet
bandwidth_cost = GB_used × price_per_GB
ip_cost = allocated_IPs × price_per_IP
total_cost = bandwidth_cost + ip_cost + request_fees + operating_cost
cost_per_successful_task = total_cost ÷ successful_tasks
Model | Hypothetical billing input | Hypothetical usage | Hypothetical total | Hypothetical successes | Cost per success |
|---|---|---|---|---|---|
Rotating residential | $4 per GB | 25 GB | $100 | 900 | $0.111 |
Static residential / ISP | $8 per IP | 10 IPs | $80 | 850 | $0.094 |
Datacenter | $2 per IP | 10 IPs | $20 | 800 | $0.025 |
The example isolates one billed resource for readability. Real plans may combine bandwidth, IP allocation, requests, minimum commitments, replacements, and support. Include engineering and retry costs, then compare cost per successful task rather than unit price alone.
When these proxy models are not suitable
- Do not use any proxy when the target or data is not authorized, or when an approved API or export already provides the required data more reliably.
- Do not choose residential or ISP origin when the only need is a stable allowlisted corporate egress; a dedicated datacenter IP is simpler.
- Do not use per-request rotation for a workflow whose login, transaction, or QA state expects one source IP.
- Do not use one static endpoint for broad regional sampling when one location cannot represent the required markets.
Pre-purchase checklist
- Write down whether network origin is a real requirement and which countries, states, or ASNs matter.
- Set the required session length and choose rotating, sticky, or static behavior separately.
- Confirm protocol, authentication, sharing or dedication, concurrency, traffic limits, and replacement policy.
- Model bandwidth and IP fees, then pilot enough requests to measure successful tasks, retries, latency, location accuracy, and operator time.
- Document authorization, rate limits, data minimization, retention, and credential handling before production use.
Security, privacy, and compliance
- Use only permitted targets and data. A new exit IP does not create authorization.
- Review residential-node sourcing, consent, withdrawal, and abuse handling.
- Protect credentials, separate workloads, cap concurrency, and redact secrets from logs.
- Minimize personal data and retain only what the approved purpose requires.
- Treat IP geolocation and proxy classification as estimates that can change.
Frequently asked questions
Is a static residential proxy always the same as an ISP proxy?
Often, but there is no universal product standard. Verify the network registration, hosting, allocation, and replacement policy.
Can dynamic residential proxies keep one IP?
Many support a sticky session for a limited period, but continuity still depends on node availability and provider limits.
Are datacenter proxies always static?
No. Datacenter describes the network source. The service may provide fixed, shared, dedicated, or rotating addresses.
Which type is fastest and cheapest?
Datacenter products often have simpler paths and lower cost, but there is no universal guarantee. Benchmark the actual route and workload.
Can residential exits guarantee access?
No. Destinations can classify residential proxy addresses and use many other signals. Follow their approved interfaces and policies.
Compare MIYAIP proxy options
Start with the simplest proxy model that satisfies your authorized workflow, then validate it with representative traffic.